SOC 2 · HIPAA · ISO 27001
We don't sell platforms. We earn audits.
SOC 2 readiness for companies whose buyers have started asking for a report.
Your buyers are asking for a SOC 2 report and your engineers are asking who owns it. We take you from first gap assessment to auditor handoff with fixed pricing, operator-led delivery, and no platform to buy.
Before you buy anything
Three jobs, three parties
Compliance software, readiness consultants, and audit firms do different work. Buyers are routinely sold one as though it were the others, and that is where SOC 2 budgets get wasted.
The platform collects the proof
Vanta, Drata, Secureframe and others connect to your systems and gather evidence automatically. That is real work and it saves real time. It is also the part most people think is the whole job.
The consultant decides what is worth proving
Which controls actually fit your business, whether your evidence would survive a sampler pulling it, and what the auditor will ask that no dashboard ever will. A platform can tell you a control is failing. It cannot tell you whether it was the right control for your business in the first place. This is the job we do.
The auditor independently tests it
A licensed CPA firm performs the examination and issues the report. They cannot design what they attest to, which is why readiness and audit are separate purchases. We are not an audit firm and we never grade our own work.
You do not always need all three. You do need to know which one you are buying.
SOC 2 Readiness
The readiness ladder
Start where you are. Every engagement is remote, fixed-scope, and priced for teams without a compliance department. If you are not sure which rung you are on, the first one answers that for $2,500 and credits back if you go further.
Start here
Readiness Diagnostic
2 weeks · we do the work
An independent read of where you actually stand.
- ·Every criterion marked real, asserted, or missing
- ·A re-derivation of whatever you already believe is done
- ·The three or four findings that would become audit exceptions
- ·Credits in full against a larger engagement within 60 days
Coach
SOC 2 Readiness Coaching
4 to 8 weeks · your team drives
Your team owns the work. We keep it on track.
- ·Office hours and document review
- ·Control guidance as you build
- ·Auditor liaison support
- ·Your own AI assistant set up to work the checklist with you
- ·For founders and engineers carrying it themselves
End to end
Full SOC 2 Readiness
12 to 16 weeks · we drive end to end
We drive it end to end.
- ·Policies and control implementation
- ·Evidence collection and vendor reviews
- ·Pre-audit walkthrough
- ·Clean handoff to the audit firm
- ·AI-drafted documentation, human reviewed
Retainer
Managed Compliance
Rolling · after your audit
Your Type II window opens the day after your as-of date.
- ·The compliance calendar runs, obligations open on schedule
- ·Criteria re-validated on cadence, with a written record of what was examined
- ·Security questionnaires answered from a maintained library
- ·Three tiers, $1.5K to $5K a month
- ·Or prepaid hours instead: 10 for $1,500, 20 for $2,800
Need help past a coaching scope, or just someone to call after your audit? Prepaid hours: 10 for $1,500 or 20 for $2,800, used within 12 months.
We are not an audit firm and do not issue SOC 2 reports. Readiness and advisory only, by design: nobody should audit their own work. When you are ready, we refer you to a licensed CPA firm and support you through the audit.
Not sure what you actually need?
Email us two paragraphs: what you sell, and what your buyer is asking for. We will tell you honestly whether you need coaching, full readiness, or nothing yet. No call required.
Get an honest readHow payment actually works
Nothing is due the day you sign. Engagements are invoiced against delivery, and every invoice is net 30 by ACH. On a Full Readiness engagement that is 50% invoiced at signature and payable thirty days later, 25% when your first two deliverables are accepted, and the last 25% when your auditor begins fieldwork.
Audit fees are separate and are not ours. The report comes from an independent licensed CPA firm you engage directly, and you pay them directly. For a Type I at this size budget roughly $10,000 to $20,000, and expect real quotes to land outside that in both directions. We take nothing from any firm we introduce, and we will tell you that range before you ask.
The Client Portal
Your engagement, visible.
Every engagement runs through a live client portal: control-by-control readiness across your Trust Services Criteria, the phase timeline with real dates, and a running engagement log of everything that has happened. You watch your audit readiness move instead of waiting for a status meeting.
- ✓Live control statuses, from client-asserted to independently validated
- ✓Phase timeline that moves when the plan moves, with your audit date always in view
- ✓A dated engagement log, so the record of the work is never a mystery
- ✓Evidence pointers only, never your raw artifacts: sensitive material stays in your environment
Reported is not validated.
Most compliance tooling collapses those two into one green square. Reported means you told us a control is in place. Validated means we read the criterion, looked at your actual evidence, and concluded it holds. The gap between them is where audit exceptions live, and closing it is the engagement.
So every criterion in your portal carries the method before anyone touches it: what proves it, how we test it, and the population that would make it a finding. You can see what we intend to do to a control before we do it.
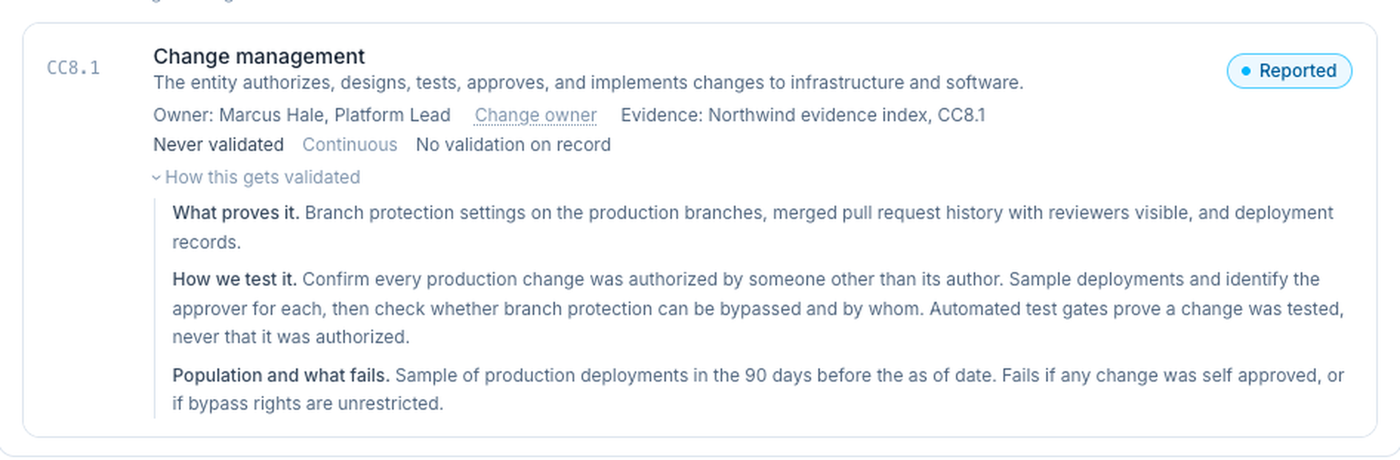
No login, no form. Sample data, not a client's.
Regulated Buyers
Selling into universities, health systems, or the enterprise?
SOC 2 is rarely the whole ask. Regulated buyers layer their own obligations on top: HIPAA for health data, FERPA for student records, ISO 27001 for international and enterprise deals. We map them into one control set so you build one program, not three.
SOC 2 + HIPAA
ScopedHealthcare and healthtech buyers
We map Security Rule safeguards and business associate obligations onto the same control set your SOC 2 runs on, so the overlap gets built once.
What healthcare buyers check beyond the report →Ed-tech + FERPA
ScopedUniversity and K-12 procurement
Student-record obligations, data governance language for institutional contracts, and the security questionnaires university procurement sends before a pilot becomes an adoption.
What university procurement actually checks →SOC 2 + ISO 27001
ScopedEnterprise and international deals
When larger buyers ask for ISO certification alongside your SOC 2 report, we extend the program rather than starting over. Shared controls, one evidence pipeline.
Which one your buyers actually require →Selling into banks or fintechs? A SOC 2 report shortens that review, it does not end it. Expect a several hundred question workbook, your penetration test and continuity plans by name, and contract terms negotiated by people who negotiate them constantly. What bank vendor review asks for →
Shipping AI features? Buyers are starting to add AI questions to the same security reviews. That work has its own inventory, controls and evidence, so we run it as a separate practice called Assay. See Assay →
Engagement Timeline
What Full Readiness actually looks like.
Four phases, explicit deliverables, an end-of-phase checkpoint every time. No floating timeline, no scope creep.
Weeks 1 to 3
Scope and gap
- · System description drafted
- · Trust Services Criteria gap assessment
- · Type I vs Type II sequencing plan
- · Platform decision, if any
Weeks 4 to 7
Controls built
- · Policy set drafted and adopted
- · Access, logging, and change controls implemented
- · Vendor management stood up
- · Human review on every artifact
Weeks 8 to 12
Evidence collected
- · Evidence mapped to every control
- · Remediation support where gaps remain
- · Vendor and subprocessor reviews
- · Internal dry-run walkthrough
Weeks 13 to 16
Auditor handoff
- · Audit firm referral and selection
- · Pre-audit walkthrough
- · Evidence package delivered
- · Support through the audit window
"Audit dates are deadlines, not aspirations. We treat them that way."
Why Control and Function
Most readiness firms write policies. We get you through the audit.
Operational, not advisory
The practice was built on running compliance as the operator, not observing it as a consultant. At a prior company, we led one SOC 2 Type I program end to end as the sole IT operator, with no outside MSP and no compliance platform, and the auditor passed it clean on the first attempt. We answered buyer security questionnaires ourselves in that role. We know what an auditor will press on and where companies waste cycles.
Built for teams without a compliance department
In a company without a compliance function, security lands on the engineering lead's desk. The compliance platforms assume you have a dedicated compliance manager. You do not, and you should not need one. We deliver done-with-you readiness priced for your size.
IT, security, and compliance under one roof
We can configure SSO and talk to engineers in their own language, not just write the policies. Faster engagements, fewer escalations, and a delivery cadence technical teams respect.
AI-accelerated, human-reviewed
Policy sets and system descriptions eat consultant hours when drafted by hand, and firms bill accordingly. Our AI-assisted documentation pipeline compresses that work to days, with a human reviewing every artifact before it carries our name.
Platform-neutral, always
Our partner relationships with the major platforms get you partner pricing you cannot get going direct. Some vendors also pay us a referral fee when a client we introduce signs. We disclose it in writing before it is earned, and it never decides the recommendation. Audit firms pay us nothing, ever. The neutrality comes from experience, not distance: we have hands-on Secureframe experience and speak the others fluently. If a platform genuinely fits your environment we will implement it with you. If it does not, we will say so and save you the subscription.
Never the auditor
SOC 2 reports are issued by licensed CPA firms, and we are not one by design. We prepare you, point you to licensed audit firms, and hand off cleanly. We take no referral fee from any of them, so our recommendation has no revenue attached. We never audit our own work. That separation protects your report.
FAQ
The questions every buyer asks first.
What does SOC 2 readiness cost?+
A Readiness Diagnostic, an independent read of where you actually stand, is $2,500 and credits in full against a larger engagement within 60 days. Readiness coaching starts at $8,000 for teams that will drive the work themselves. Full readiness, where we drive the program end to end, starts at $15,000. Managed compliance retainers run $1,500 to $5,000 per month after your audit, and dual-framework engagements are scoped individually. Engagements are fixed fee, invoiced by milestone, payable by ACH or card. If you would rather have someone to call than a project, prepaid hours are available: 10 hours for $1,500 or 20 for $2,800, used within 12 months. No open ended hourly meters.
Do you perform the SOC 2 audit itself?+
No. SOC 2 audits are performed by licensed CPA firms. We provide readiness and advisory services only: we prepare you, refer you to audit firms (taking no referral fee), and support you through the audit window. We never audit our own work. That separation protects the integrity of your report.
How long does it take?+
A full readiness engagement typically runs 12 to 16 weeks from kickoff to auditor handoff. Coaching engagements run 4 to 8 weeks. One planning reality worth knowing early: audit firms book fieldwork 2 to 3 months out, and the fourth quarter is their busy season, so the audit date drives the schedule more than the readiness work does.
Type I or Type II?+
A Type I covers control design at a point in time; a Type II covers operation over a period, usually 3 to 12 months. When a deal or procurement gate needs paper soon, Type I first is the right call. When nothing is gating, many companies now go straight to a Type II over a short observation window and skip one audit fee. We will tell you honestly which fits your situation, including when the answer saves you money with someone else.
Do we need Vanta, Drata, or Secureframe?+
Not necessarily. Compliance platforms automate evidence collection well for some environments and poorly for others. Our advice stays platform-neutral, and our partner relationships with the major platforms get you partner pricing you cannot get going direct. Some vendors also pay us a referral fee when a client we introduce signs; we disclose it in writing before it is earned, and it never changes the recommendation. If one fits your stack we will implement it with you, and if not, the one SOC 2 Type I our operator led at a prior company used no platform at all and passed clean on the first attempt.
Can you handle HIPAA, FERPA, or ISO 27001 alongside SOC 2?+
Yes. Healthcare buyers bring HIPAA, education buyers bring FERPA and the HECVAT questionnaire, and international or enterprise deals often ask for ISO 27001. We scope the SOC 2 work to map these into a single control set, so you build one program instead of three. Selling into universities? Read what university procurement actually checks.
Vendor reports: what Complementary User Entity Controls are, and why holding a vendor’s SOC 2 is not reviewing it.
Contact
Start the conversation.
A 30-minute readiness call costs nothing and tells you exactly where you stand, whether it is your first SOC 2 or a second framework on top of it. No sales pressure. If we are not the right fit, we will say so and point you to someone who is.